Vavada официальный сайт игры клуб
August 4, 2024Example Post for WordPress
August 14, 2025Mix SAST/DAST, dependency and TLS config scanners, secret-scanning, and manual reviews. Add unit/integration exams for crypto settings (e.g., enforcing TLS, blocking weak ciphers). Hard-coded keys/secrets, weak/random-looking but predictable PRNGs, IV/nonce reuse, accepting invalid TLS certs, mixed content (HTTP on HTTPS pages), and failing to rotate keys. Use salted, adaptive hashes (Argon2id or bcrypt; PBKDF2 with high iterations). Begin a free trial or guide a demo to see how Codacy can enhance your security. No cryptographic technique is complete without regular safety audits and penetration testing.
- Codacy ensures your code adheres to cryptographic greatest practices, giving builders real-time suggestions to resolve points before they escalate.
- These computer systems contained sensitive employee knowledge, together with names, Social Safety numbers, and checking account details.
- By distinction, insecure APIs could leak sensitive information if tokens or credentials aren’t properly encrypted or validated, doubtlessly opening the method in which to large-scale automated exploitation.
- Additionally, it underlined important components on broad safety testing and auditing to detect and proper seen areas prone to be used by hackers.
Owasp High 10: Cryptographic Failures
Cryptography is a large topic with dedicated consultants, but that doesn’t imply developers can depart it entirely to their security teams. Building security into DevOps means you should perceive how to ship secure, high-quality code at velocity. To assure an immediate response to a cryptographic failure, organizations should put in place effective breach response mechanisms. To defend the clients’ data, organizations should, nay, must be certain that they keep a close eye on the entire knowledge they retailer throughout the system(s). This way, they may at all times have the power to maintain observe of the homeowners, locations, security, as nicely as governance measures which would possibly be enabled on the saved knowledge. Of course, when sites don’t enable HTTPS security and don’t secure the connection by way of SSL, the web pages and apps that store delicate info will all the time be weak.
Compliance

You also can think about a state of affairs the place the credentials of an admin are stolen and the attacker gets full management of a server. Cryptographic failures can lead to irreparable damage to popularity and heavy lawsuits. It’s any weak point caused by lacking, weak, or misused cryptography that exposes sensitive data—e.g., no TLS, outdated ciphers, poor key handling, or weak password hashing. A single cryptographic weak point can result in publicity of credentials, id theft, unauthorized access, and full-scale knowledge breaches.
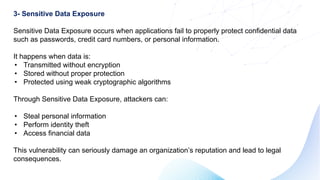
Cryptographic Failures: An Owasp Prime 10 Risk
Unlike static instruments that spotlight theoretical risks, using a vulnerability scanner with a DAST-first approach focuses on real-world exposure, such as unencrypted endpoints, damaged HTTPS enforcement, or misconfigured headers. By validating findings via proof-based scanning, DAST reduces false positives and helps prioritize remediation of precise risks, permitting small groups to safe their applications extra successfully. These points usually stem from implementation or configuration flaws quite than issues with the cryptographic algorithms themselves. Because cryptography protects sensitive information, any failure can expose info to malicious actors and result in extreme safety breaches. To perceive https://tvsubs.net/episode-117809.html cryptographic failures, it could be very important first perceive cryptography.
Cryptographic functions could be implemented insecurely, leading to vulnerabilities. Kaycie Waldman works intently with SaaS, cloud, and technology organizations on security, danger, and compliance initiatives that assist development and enterprise readiness. Her work spans strategic content material, go-to-market initiatives, and buyer trust packages designed to assist scale, compliance, and enterprise sales. With powerful tools and techniques, unsalted hashes aren’t very tough to crack. Password salting makes it difficult for any password cracking technique as the salt adds further length to the password. Nevertheless, If you’re storing unsalted passwords, an attacker can use a rainbow desk to crack these passwords.
